

Continuous, Agentic-AI PCI-DSS Penetration Testing for Modern Payment Environments
Fulfilling PCI-DSS requirements doesn’t have to delay deals or stifle growth. Penti delivers PCI-DSS penetration testing services that continuously verify the security of your payment environment, helping you pass audits faster, reduce risk, and prove security to customers, unlike the disruptive, one-off testing cycles of traditional pentests.


Modern PCI-DSS Penetration Testing, Built for Scale
Penti’s PCI-DSS penetration testing services are designed for organizations that process, transmit, or store payment card data and need to demonstrate real security, not just checkbox compliance. Traditional PCI-DSS pentest approaches can be expensive and outdated. An automated-only pentest can miss exploitable vulnerabilities and business-critical risks across critical systems.
Penti replaces both with Agentic-AI-driven PCI-DSS compliance pentesting, continuously testing your environment using attacker-based techniques verified by certified penetration testers. Our AI agents simulate how an external attacker would target your payment systems, identifying real security weaknesses across your cardholder data environment (CDE).
Unlike point-in-time PCI-DSS penetration tests, Penti delivers ongoing assurance that your security controls are working as intended and helps companies maintain compliance throughout the year.
Turn PCI-DSS from a Barrier into a Growth Enabler
Penti helps organizations transform PCI-DSS pentesting from a regulatory lift into a strategic advantage by solving three core business challenges:
Pass PCI-DSS Audits with Confidence
Reduce Risk to Revenue-Critical Payment Data
Accelerate Enterprise Deals and Partnerships
Continuous Testing Without Disruption
Scope & Environment Mapping
Agentic-AI Attack Simulation
Human Verification & Risk Validation
Remediation Guidance & Reporting
Continuous Assurance
How Penti’s PCI-DSS Pentesting Works
How Penti Maps to PCI-DSS 4.0 Requirement 11.4
PCI-DSS 4.0 Requirement 11.4 defines penetration testing obligations for any organization that handles cardholder data. Penti’s continuous approach covers every sub-requirement.
11.4.1: Defined penetration testing methodology
11.4.2 & 11.4.3: Internal and external penetration testing
11.4.4: Correct and re-test exploitable vulnerabilities
11.4.5 & 11.4.6: Segmentation controls testing
Penetration testing types done by Penti

API pentesting

Cloud pentesting

Network pentesting

External network pentesting

Internal network pentesting

Mobile pentesting

Web app pentesting

Penetration testing for IoT
More compliance-driven pentests by Penti

Industries we work with


Benefits of Penti’s PCI-DSS Penetration Testing Tool
Penti delivers measurable advantages over traditional PCI-DSS penetration testing providers, from continuous coverage to audit-ready reporting.

Continuous PCI-DSS Pentesting

Human-Verified, Audit-Ready Results

Real-World Attack Focus

DevOps-Ready & Scalable
Trusted by Security & Compliance Leaders
Built for Teams Accountable for Risk and Revenue
CISOs, CTOs, compliance leaders, and founders rely on Penti to protect cardholder data, strengthen security posture, and demonstrate trust to customers and auditors.


Penti's service is a game changer for our compliance needs. The insights we gained were invaluable for our team. Doing this well is crucial for our compliance targets and key in advancing our strategic initiatives.

The integration between Penti, our system, and third parties like Vanta is exceptional. I would also like to mention that their response times are extremely fast!

Penti has been like having an experienced and nimble Security Engineer on staff. They have outlined issues in our platform and guided us towards implementations and fixes that allow for us to ensure we are treating our users data with the utmost care.
Why Choose Penti for PCI-DSS Pentesting?
Security Assurance, Not Just a Pen Test

Penti stands apart from traditional penetration testing providers by redefining what PCI-DSS pentesting should deliver: continuous assurance instead of point-in-time snapshots.
Agentic-AI with Human Expertise
Combines intelligent automation with expert validation from certified penetration testers for accuracy and depth across the entire cardholder data environment.
Designed for Continuous Protection
Supports continuous monitoring and ongoing threat detection instead of once-a-year testing frequency.
Aligned to Real-World Risk
Focuses on identified vulnerabilities that pose genuine business impact, prioritized by exploitability to strengthen your organization’s security posture.
Faster, More Cost-Effective Compliance
Reduces reliance on repeated manual testing and fragmented assessments, streamlining your PCI-DSS compliance journey and internal testing efforts.
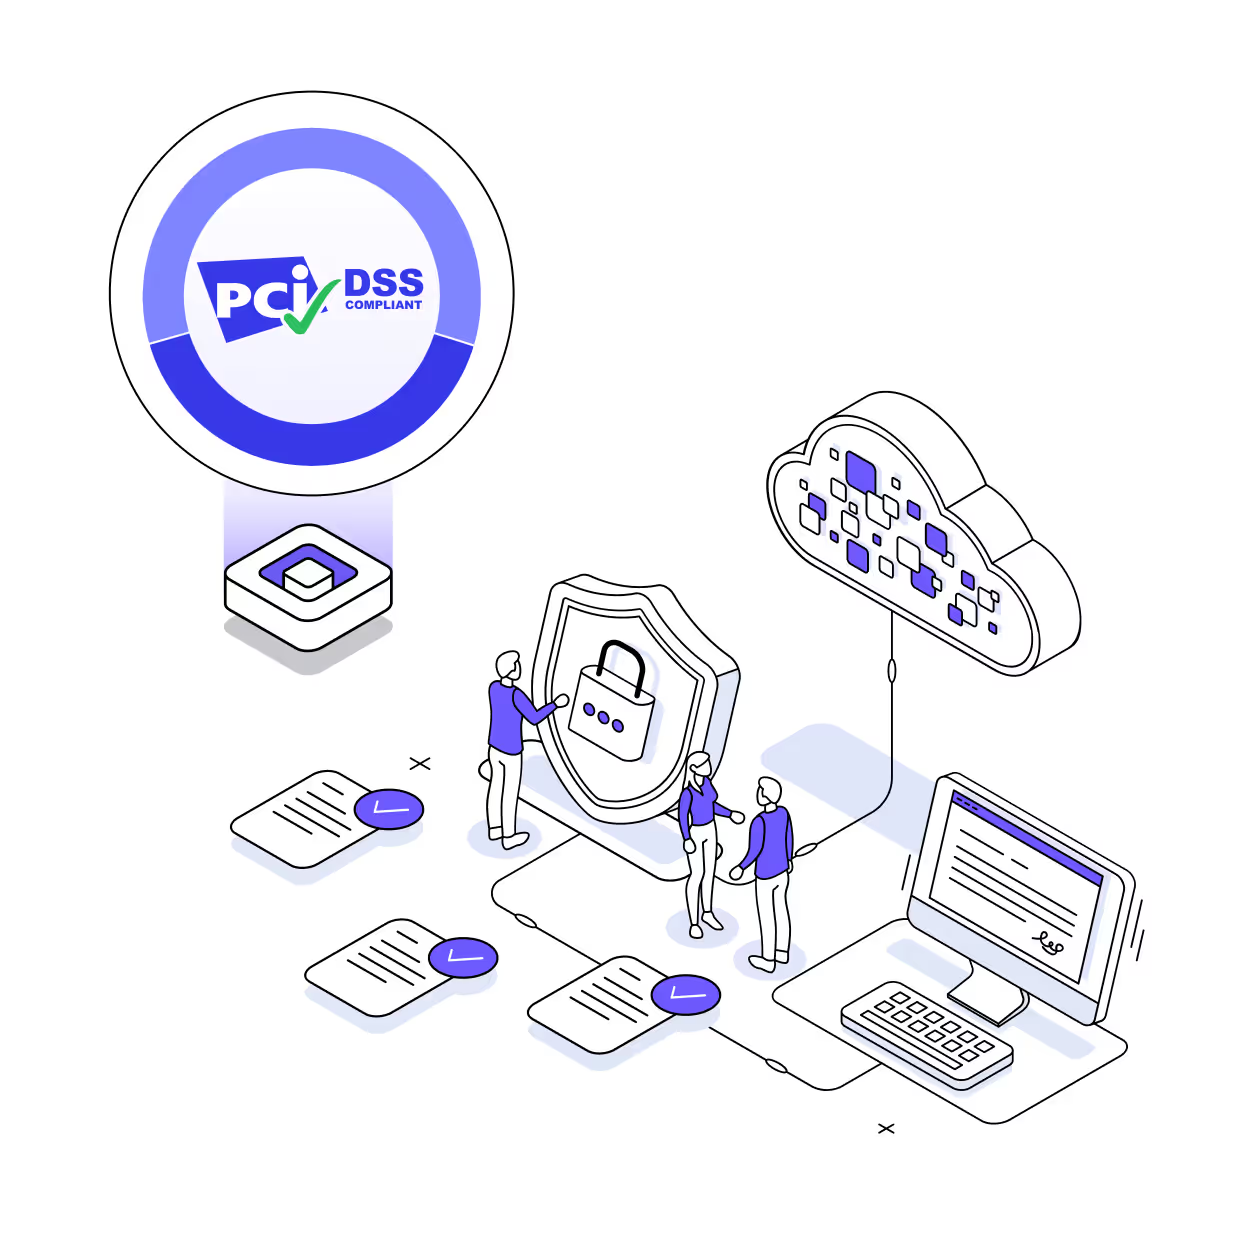
Fits into your compliance stack
Penti connects with the tools your compliance and security teams already use, so PCI-DSS pentest findings flow directly into your audit workflows and remediation efforts.
Vanta
Drata
Slack
Cloud Providers






FAQ
What is a PCI-DSS penetration test?
A PCI-DSS penetration test evaluates the security of systems that store, process, or transmit credit card data to identify exploitable security weaknesses across the cardholder data environment. It satisfies PCI-DSS Requirement 11.4.
How often should PCI-DSS pentesting be performed?
PCI-DSS requires testing at least annually and after any significant changes to infrastructure or applications. Continuous testing provides stronger assurance and easier audit preparation than one-off annual cycles.
Does Penti replace traditional PCI-DSS pentest vendors?
Yes. Penti delivers equivalent and deeper coverage with continuous testing and human verification.
Is Penti suitable for complex payment environments?
Absolutely. Penti supports segmented networks, wireless networks, hybrid cloud environments, and complex payment data flows across the entire cardholder data environment.
Does Penti support both internal and external testing?
Yes. Penti performs external penetration testing and internal network attack simulations aligned to PCI-DSS 4.0 Requirements 11.4.2 and 11.4.3, plus segmentation testing per 11.4.5.
Will Penti help with audit readiness?
Yes. Reports are designed to support auditors, QSAs, and internal stakeholders, with detailed documentation mapped to PCI-DSS requirements.
What are PCI-DSS 4.0 penetration testing requirements?
PCI-DSS 4.0 Requirement 11.4 mandates a defined penetration testing methodology (11.4.1), internal and external testing at least annually and after significant changes (11.4.2, 11.4.3), correction and re-testing of exploitable vulnerabilities (11.4.4), and segmentation controls testing where implemented (11.4.5). Service providers have additional obligations under 11.4.6 and 11.4.7.
What is the difference between PCI-DSS penetration testing and vulnerability scanning?
A vulnerability scan uses automated tools to identify known weaknesses across your systems. PCI-DSS requires quarterly external scans performed by a PCI Approved Scanning Vendor (ASV). Penetration testing goes further: certified experts (or AI agents backed by human review) actively exploit vulnerabilities to prove real risk. PCI-DSS requires both, and they serve different purposes.
Do I need a Qualified Security Assessor (QSA) for PCI-DSS penetration testing?
No. PCI-DSS does not require a QSA to perform the penetration test itself. It requires a qualified penetration tester with documented methodology and independence from the systems being tested. QSAs are needed for the formal PCI-DSS assessment (Report on Compliance), not the pentest itself.
Is PCI-DSS compliance mandatory for my business?
Yes, if your business stores, processes, or transmits cardholder data. PCI-DSS is a contractual requirement from the card brands (Visa, Mastercard, Amex, Discover, JCB), enforced through your merchant acquirer. Non-compliance can result in fines, higher processing fees, and loss of the ability to accept card payments.